Enabling access to XML-RPC
Public access to the XML-RPC file (xmlrpc.php) on our servers is blocked by default, because the file is a common target for hackers. More details are available in our Error "412 Precondition Failed" (mod_security2) article. You can now easily enable access to it by following these steps:
1. Open the WordPress Manager in the hosting Control Panel.
2. Find the WordPress installation in the list, and click on the Manage button for it. This will take you to the management page for the WordPress installation.
3. Scroll down to the Security section, and locate the option called Enable access to XML-RPC.
4. Click on the Enable toggle next to it.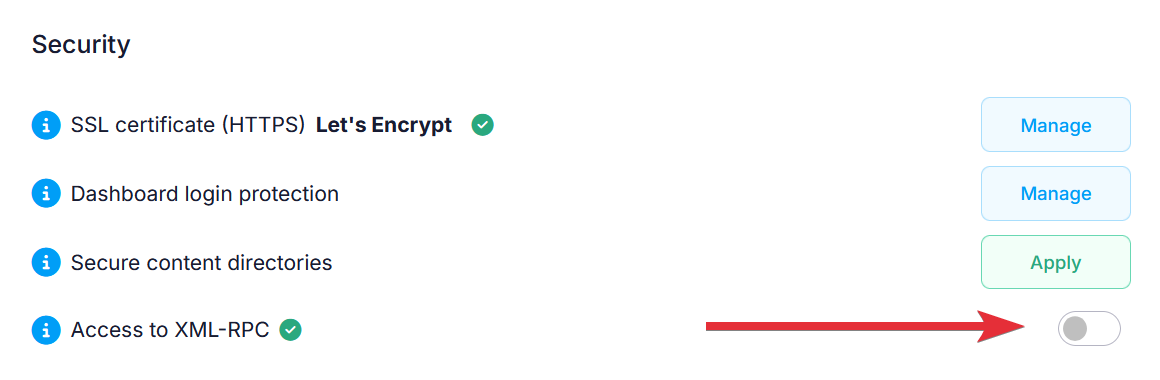 This is it - you can now successfully install and use any plugin that requires access to XML-RPC.