Modifying a mailbox quota
All email accounts are created with a predefined quota, depending on the hosting plan of the account. You can modify the disk space quota and the maximum allowed messages (inode quota) as needed.
To adjust the disk quota for a given email account, please follow these steps:
- Go to the Mail Manager section.
- Click the checkbox under the Quota or the Messages column next to the email account.
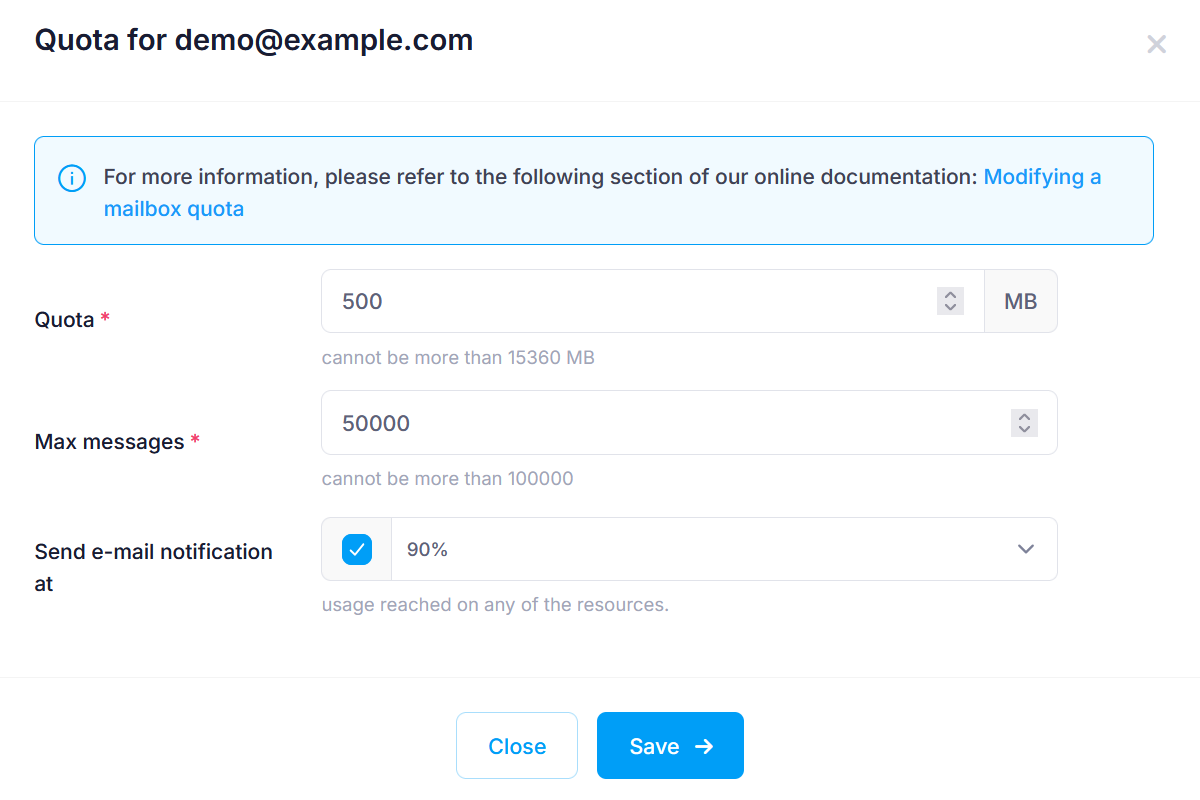
- You can customize the following settings:
• Quota: Enter the maximum disk space in megabytes (MB).
• Max messages: Set the maximum number of stored messages.
• Send e-mail notification at: Choose the usage percentage that will trigger a warning email when the email account is nearing its limits. - Click Save.
Note: Besides the custom quota notification, our system will always send a notification at 99% usage reached - this "99% usage" notification cannot be stopped/adjusted.